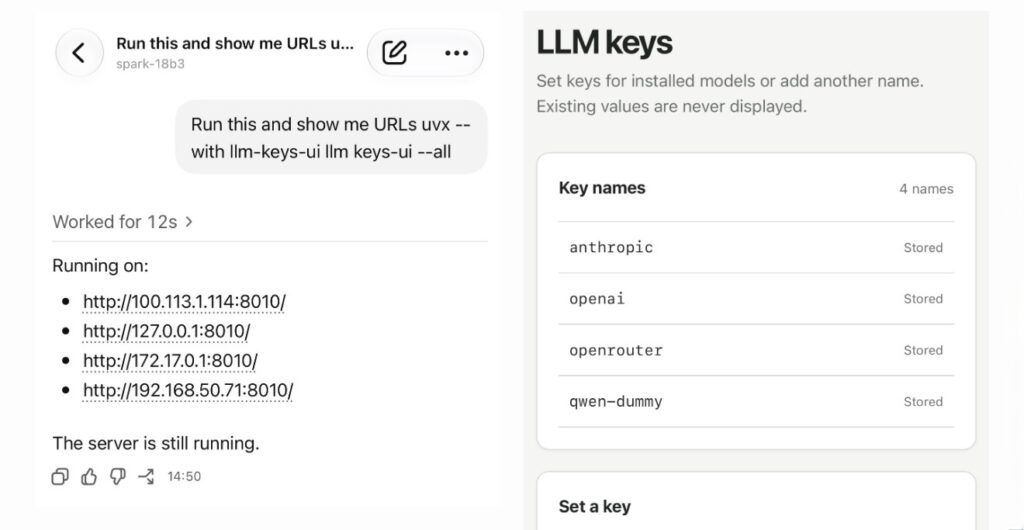
Simon Willison released llm-keys-ui 0.1 to address the security risk of pasting API keys directly into coding agent sessions. He uses Codex Remote to run agents on remote machines while controlling them from his phone, a workflow that occasionally requires configuring new API keys for LLM projects. The plugin allows the agent to execute a command that starts a local web interface for storing credentials without exposing them in the chat log. Users can then retrieve specific keys via shell commands when the agent needs to authenticate.
This tool solves a practical problem for developers managing remote coding environments who need to keep sensitive data separate from their conversation history. It prevents accidental key exposure in logs or screenshots while maintaining a secure method for agents to access necessary services.
* The interface displays stored keys for providers like Anthropic, OpenAI, OpenRouter, and Qwen without showing their actual values
* Keys are saved via a form containing fields for name and new value
* The server runs on port 8010 and remains accessible via local network or Tailscale device IPs