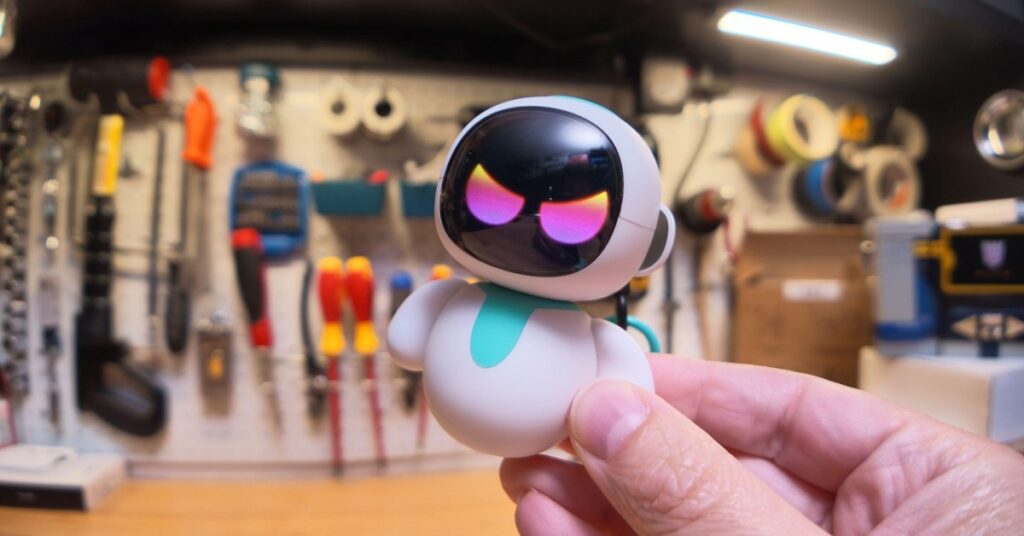
Energize Lab has confirmed it is hiring an independent security firm to address flaws in the Eiliko robot toy after The Verge reported that hackers could access private user conversations. The device, marketed as a secure AI companion, allowed attackers to read full transcripts of chats stored on the hardware. The company initially remained silent for over a month despite repeated attempts by reporters and security researchers to contact founder Shaw Yeung.
The statement released by Energize Lab admits the core issues exist but does not provide a timeline for a fix or details on how the data was compromised. This delay highlights a disconnect between consumer trust in AI devices and the reality of their implementation. The incident raises questions about whether similar toys will receive adequate oversight before reaching other markets.
* The breach exposed complete conversation logs stored locally on the device.
* Energize Lab has not specified when the security patch will be deployed.
* No explanation was given for the lack of response during the initial investigation.